Types of Mobile Phishing in 2026
Last updated 8 Sep 2026
Mobile phishing is any attempt to steal credentials, session tokens, payment details or data by delivering a lure to a phone or tablet. The delivery channel is what distinguishes it from email phishing, and the channel is the reason most enterprise security stacks never see it.
ENISA’s Threat Landscape 2025 found phishing to be the dominant intrusion vector, accounting for approximately 60% of cases. Vulnerability exploitation represented 21.3% of initial access vectors and malicious applications 8%.
What channels do mobile phishing attacks use?
Eight channels account for most of the mobile phishing an enterprise will encounter.
1. Smishing (SMS, RCS and iMessage)
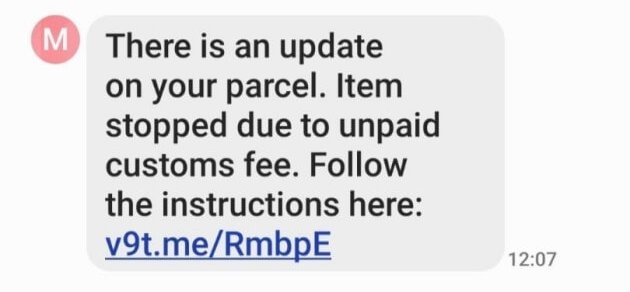
Smishing is phishing delivered by text message. The employee receives a message that prompts a tap, and the link either loads a credential-harvesting page or starts a download.
Attackers have moved beyond SMS to RCS on Android and iMessage on iPhone. Both travel over the internet rather than the carrier network, which puts them outside the SMS filtering operators apply to scam traffic.
Because iMessage suppresses links from unknown senders, a common workaround is to ask the recipient to reply first. The reply establishes a two-way conversation, which re-enables the link and confirms the number is live.
Common enterprise pretexts include payroll and HR portal changes, IT password expiry notices, missed parcel deliveries, toll charges and tax refunds.
2. Quishing (QR code phishing)
Quishing uses a QR code to carry the malicious URL. It works because the destination cannot be read before the scan, and because the scan usually moves the victim from a managed corporate endpoint to a personal phone with none of the same controls.
The typical enterprise sequence starts on the desktop. A message arrives with a code and a pretext, often MFA re-enrolment, a payroll form or a compliance acknowledgement. The employee scans it with their own phone, the phishing page loads in a mobile browser, and the credentials are entered somewhere the organisation has no visibility at all.
Two variations are worth knowing about. Dynamic codes can point at a harmless page while the message passes through filtering, then be re-pointed afterwards. Physical codes get overlaid with stickers on parking meters, menus and posters, so the printed context looks legitimate.
3. Messaging and collaboration apps
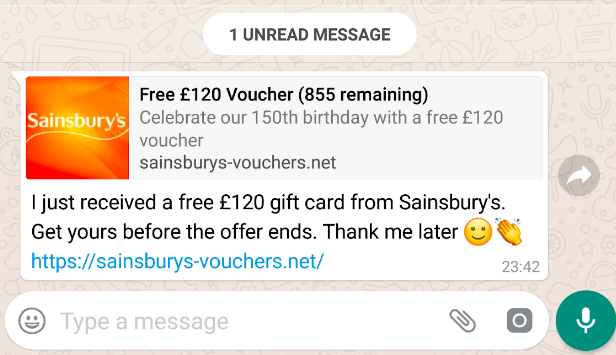
WhatsApp, Telegram, Signal, Microsoft Teams and Slack all carry phishing, and all of them are on the phone.
The pattern here is conversational rather than transactional. An attacker impersonates a colleague, a supplier or an executive, or opens with a plausible wrong-number message and builds familiarity before making an ask. Group invitations are used to reach several employees at once.
The defensive problem is structural. Message content in these apps is end-to-end encrypted, so there is no upstream point at which a gateway can examine a link. The only place the link can be assessed is the device itself.
4. Social media and recruitment lures
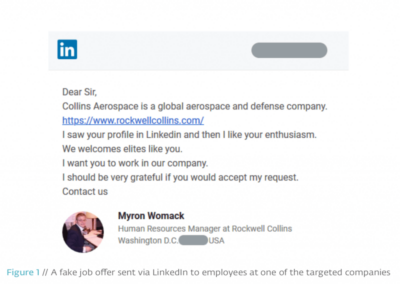
Phishing on social platforms reaches employees through direct messages, comments, spoofed company pages and paid posts. LinkedIn matters most in a B2B context, because an attacker can read someone’s role, seniority and reporting line, then tailor the approach. Fake recruiter outreach works for the same reason, since the target expects an attachment or a portal login.
Corporate logging sees none of this. The account is personal, the app is personal, and the phone is frequently both personal and work-enabled.
5. Vishing and callback phishing
Vishing is phishing by voice, and ENISA counts it within the approximately 60% of cases attributed to phishing. Callback phishing sends a message containing a phone number instead of a link, so the victim initiates the call and there is nothing for a link scanner to catch.
This is where the simulation gap shows. The Verizon 2026 Data Breach Investigations Report recorded a median click rate of 1.4% for email phishing simulations against closer to 2% for phone-centric methods, an increase of 40% between those vectors. Awareness programmes built entirely on email simulations are measuring the channel that performs worst for attackers.
Help desk impersonation is the highest-value variant, since a convincing call to IT support asking for an MFA reset can hand over an account without any phishing page.
6. Authentication-flow attacks
Most of the channels above end at the same place, a page that harvests something reusable. What gets stolen is increasingly the session token rather than the password.
Adversary-in-the-middle kits proxy the real login page. The user sees the genuine site, enters credentials, completes MFA, and the attacker copies the session cookie issued afterwards. That cookie can be replayed from anywhere, and it is valid because the authentication genuinely happened.
These techniques are a small share of identity attacks by volume. The Microsoft Digital Defense Report 2025 found that more than 97% of identity attacks were password spray or brute force. Everything else combined, including token theft by malware, adversary-in-the-middle and consent phishing, accounted for less than 3%.
Microsoft’s framing is that modern multifactor authentication still reduces the risk of identity compromise by more than 99%, and that while attacks against identity infrastructure remain limited in volume, their variety is increasing.
That is the reason to care about a fraction of a percent. These are the techniques that work specifically against accounts MFA already protects.
Two related methods target the handset directly. Push fatigue floods the authenticator app with approval prompts until one is accepted. Device code phishing walks the victim through entering a legitimate code on a legitimate sign-in page, which authorises the attacker’s session.
7. Malicious and counterfeit apps
Malicious applications accounted for 8% of the initial infection vectors ENISA identified. They arrive by three routes.
- Official stores: App review reduces the problem without solving it. A recurring tactic is to publish something benign, build an install base, then add malicious code in a later update or pull it down through a fake in-app update prompt.
- Third-party stores and sideloading: There is no guarantee that a sideloaded package is the app it claims to be. Counterfeit builds of popular messaging apps are a persistent category.
- Permission abuse after install: Accessibility services and screen overlay permissions are how banking overlays and credential capture work in practice. Both are legitimate features with narrow legitimate uses.
8. Ads, notifications and search results
The final category has no sender at all. Browser push notification subscriptions, once accepted, deliver lures that look like system alerts. Poisoned search results put a phishing page above the real one.
Why mobile phishing succeeds where email phishing fails
A mobile browser shows a fraction of the address bar and offers no hover preview, so the URL cannot be checked before the tap, and notifications are built to be acted on immediately, usually mid-task.
The same handset holds the corporate mailbox, the family WhatsApp group and a personal LinkedIn account, and it spends most of its life on mobile data or home Wi-Fi rather than the corporate network the web gateway protects.
Built-in protection fills little of that gap, since consumer blocklists need a domain to be known bad already.
How organisations defend against mobile phishing
- Inspect links on the device, across every app, rather than only in email and the browser.
- Apply real-time domain assessment rather than static blocklists, and treat newly registered domains as suspect until they establish a reputation.
- Move to phishing-resistant MFA (passkeys or FIDO2 security keys) for privileged accounts first.
- Shorten session lifetimes and monitor for token replay, so an adversary-in-the-middle success has a limited window.
- Extend awareness training to voice and text scenarios, and give employees a channel to report a suspicious call as easily as a suspicious email.
- Maintain an inventory of installed apps and their permissions, with a policy position on sideloading.
How Corrata protects against mobile phishing
Every channel on this page ends the same way, with a connection request from the device to a server the attacker controls.
Corrata inspects that traffic on the device itself, which is what allows it to cover the channels an email gateway and a corporate web proxy never see: text messages, messaging apps, social feeds, scanned QR codes and links opened inside any app. Because inspection happens on the handset, protection travels with the device rather than depending on which network it is connected to.
Domains assessed as risky are blocked at the point the user taps, and where a device does become compromised it can be quarantined automatically and the security team alerted. Deployment does not require complex integration, and there is no change to how employees use their phones. Organisations wanting to see this against their own fleet can request a demo.
Frequently Asked Questions
Phishing is the general term for social engineering that tricks someone into revealing credentials or data. Smishing is phishing delivered by text message, including SMS, RCS and iMessage.
Smishing is the highest-volume channel. Voice-based approaches have the higher success rate per attempt: the Verizon 2026 DBIR recorded a median click rate closer to 2% for phone-centric simulations against 1.4% for email.
Yes. Phishing targets the person rather than the operating system, so a credential-harvesting page works the same on iOS as on Android.
No. Mobile device management enforces configuration, distributes apps and controls settings. It does not inspect the links arriving in a text message or a WhatsApp chat. Mobile threat defence covers that gap.
It stops most of it. Microsoft reports that modern multifactor authentication reduces the risk of identity compromise by more than 99%. The techniques in the remainder, including token theft by malware and adversary-in-the-middle proxying, exist specifically to defeat it, and each still begins with a lure that on mobile is likely to arrive outside email.