Adversary-in-the-Middle (AiTM) protection that keeps phone traffic private on any network
Most enterprise data now travels over insecure networks. Corrata keeps employee communications private on unsafe cellular and Wi-Fi…

Use case
AI lets attackers send every employee a new, personalised lure by SMS, WhatsApp, Teams, or Slack, and tools that only recognise known threats have nothing to match it against. Reflex, Corrata’s on-device threat engine, blocks the phishing site a lure leads to, even one with no prior record, without ever reading the message.

When AI can write a new lure for every employee and send it through any channel, a phone without on-device protection is a risk no organisation can afford to carry.
Today’s targeted attacks start in a text message, a WhatsApp chat, a LinkedIn post, or a Slack update, and Reflex blocks the site each one leads to.

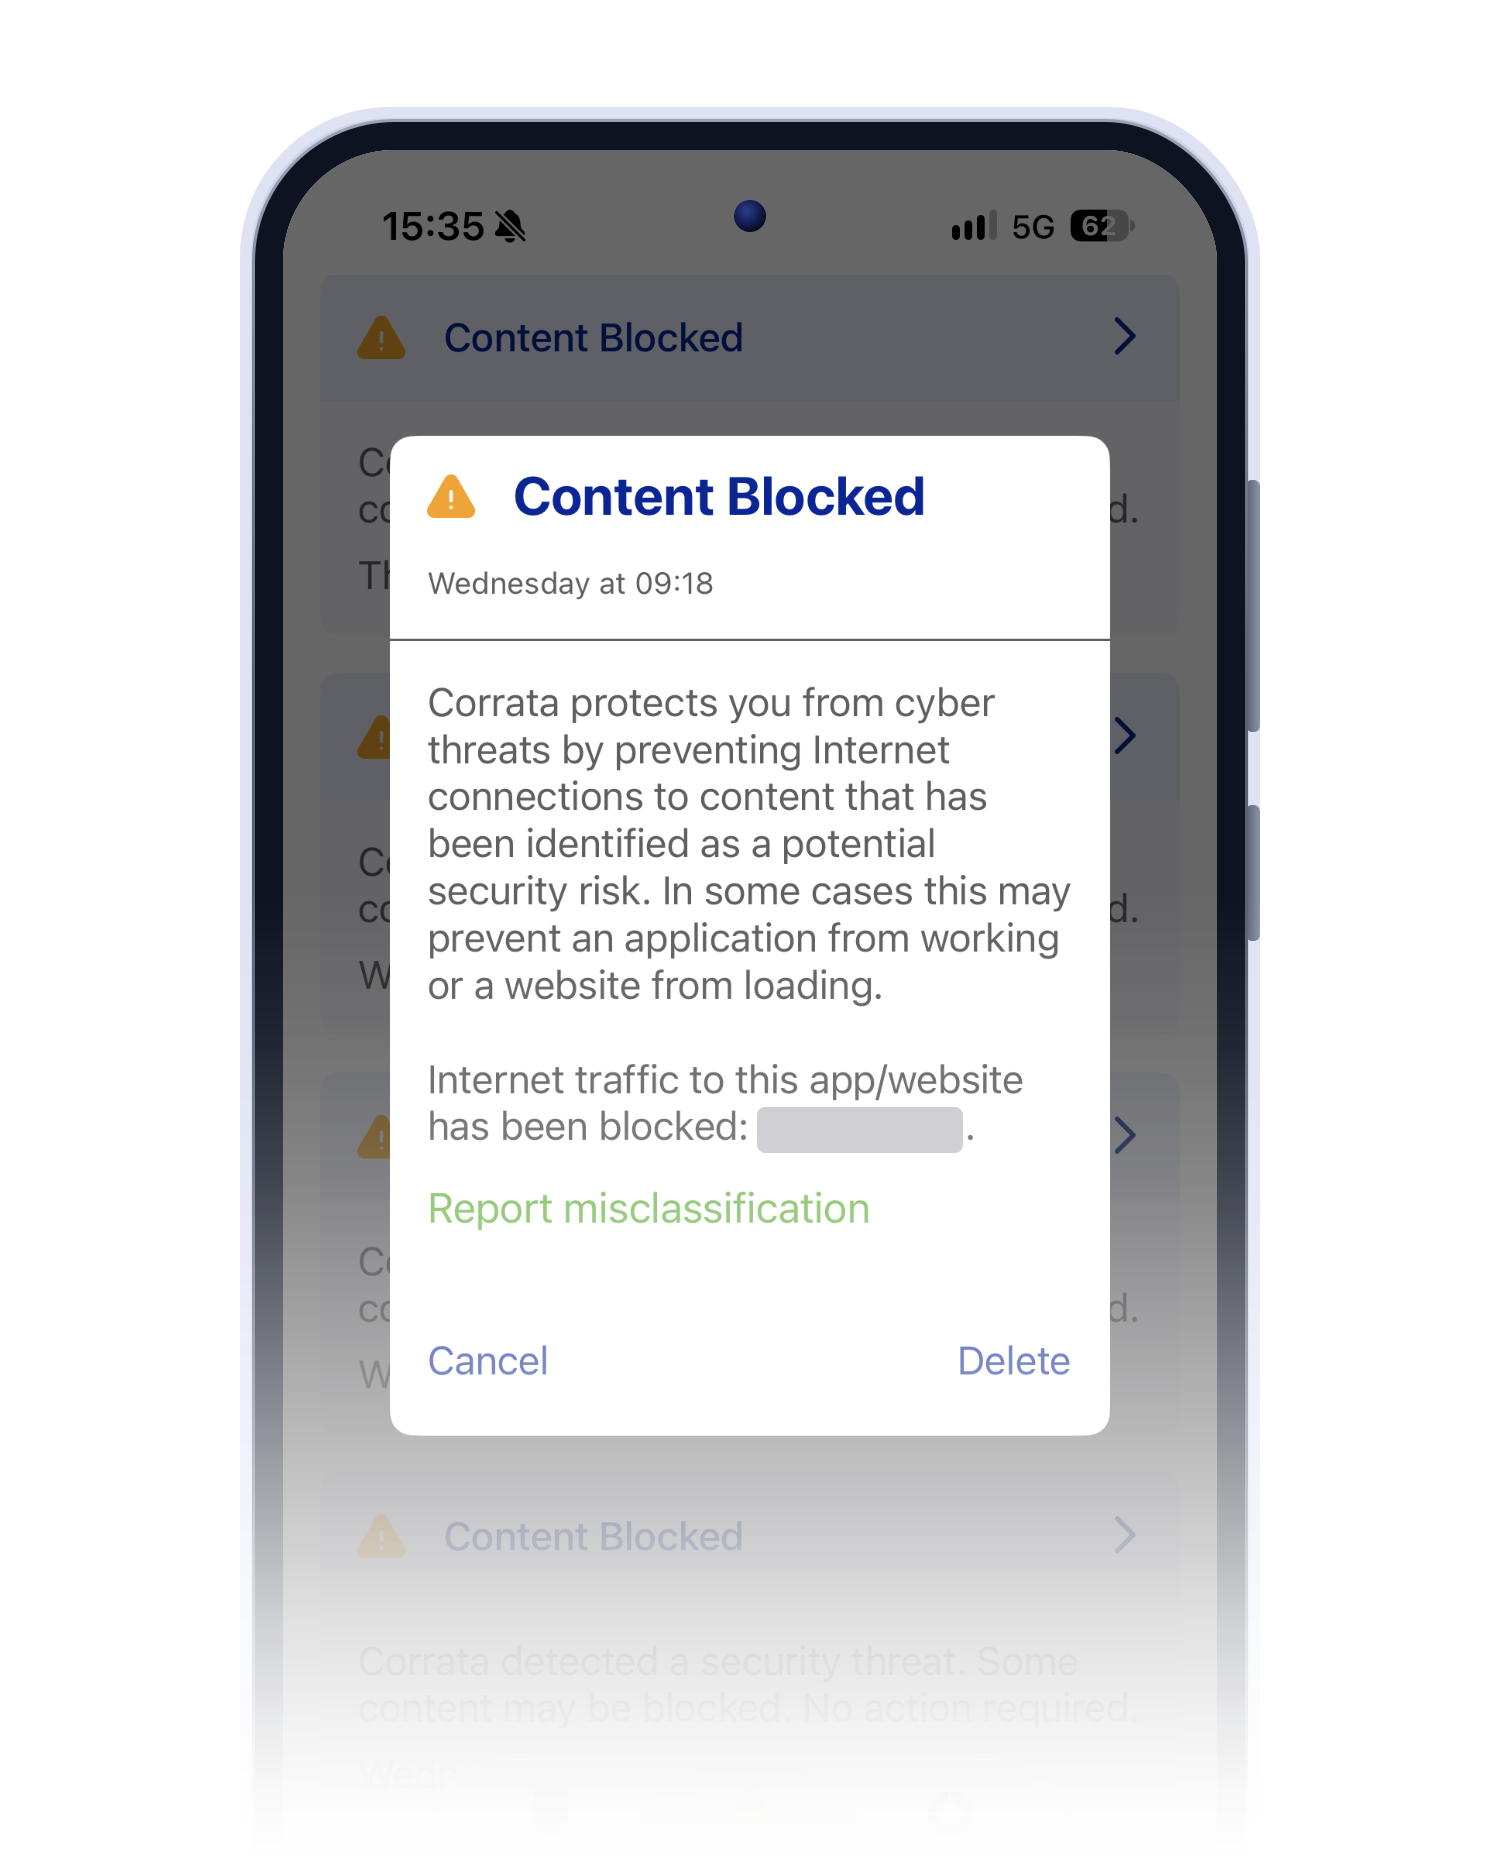
Every link an employee opens ends in a connection from the phone, whether it arrived in a smishing text, a WhatsApp chat, a QR code, a LinkedIn post, or a collaboration tool. Reflex inspects that connection on the device, reading details such as domain and server names, IP addresses, and SSL certificate metadata, and blocks it the instant it points to a phishing site. Because the decision is made on the phone, there is no wait for a verdict from elsewhere, and Corrata’s servers only receive details of the threat and the action taken.
Each connection is checked against industry threat feeds combined with Corrata’s own mobile threat intelligence. Corrata is three times more effective at blocking mobile phishing than our competitors, and 23% of the threats it detects are missed by other solutions. You can see the phishing and malware sites Corrata blocked on customer devices in the last seven days on our threat log.

A new phishing domain appears every 60 seconds, and Corrata responds in real-time.
Attackers register fresh domains so that no block list has seen them. Corrata Zero-Day Protection blocks links to domains with no established reputation until that reputation can be confirmed, so a lure set up minutes ago is stopped on the first click.
Cybercriminals buy phishing toolkits on the dark web, and Corrata stops them at the source.
90% of phishing attacks are delivered using toolkits, including adversary-in-the-middle kits that proxy the real login page to capture credentials and session cookies. By blocking access to the servers that host this infrastructure, Corrata makes the toolkit useless, however new the lure pointing to it.
Attackers hide phishing sites on legitimate website builder platforms.
Hosting a phishing page on a legitimate web platform helps it avoid detection, and several website builder platforms host a large number of phishing sites. Corrata lets you block access to any content hosted on the most abused platforms.

Reflex keeps working when DNS traffic is encrypted.
More users now hide their DNS requests using DNS over HTTPS (DoH) or DNS over TLS (DoT), which leaves DNS filtering with nothing to read. Corrata has developed a unique capability to establish the server domain from the Server Name Indication (SNI) field, so Reflex still sees where each connection is going.
Corrata adds mobile-specific research to standard industry block lists.
Most phishing threat intelligence is built around email, so many mobile security solutions lack timely intelligence on attacks that arrive by text or messaging app. Corrata’s threat research focuses on smishing and other mobile-specific threats, and Reflex combines it with industry feeds for every connection it checks.
Whitepaper
Phishing on phones arrives through text messages, messaging apps, and QR codes as well as email, and email security does not see those channels. Download the guide to understand the mobile phishing threat and how to counter it.
Phishing on mobile arrives through SMS, messaging apps, social media, and QR codes, which bypass the email security most organisations rely on. Employees are also 18 times more likely to click on a phishing link on mobile, and AI now lets attackers send each of them a lure written for them alone.
Apple and Google include consumer-grade protections against unsafe content, but they cannot keep pace with how quickly new phishing domains are generated. They are also not designed for the targeted attacks used against organisations.
Reflex makes its decision on the phone, judging what each connection is doing instead of relying only on lists of known threats, so it can block phishing sites with no prior record the moment they are reached. It combines industry threat feeds with Corrata’s own mobile threat intelligence and the enhanced protections built for mobile, including zero-day domain blocking and toolkit infrastructure blocking.
Smishing is phishing delivered by SMS text message. Attackers impersonate banks, delivery firms, or colleagues and include a link to a fake site that harvests credentials or session cookies. The same techniques now run across WhatsApp, Signal, and other messaging apps.
Reflex, Corrata’s on-device threat engine, inspects network traffic on the phone and blocks connections to malicious sites, whichever channel the link arrived through: SMS, WhatsApp, a QR code, social media, or a collaboration tool. Detection combines DNS filtering, SNI-based inspection of encrypted traffic, zero-day domain blocking, and proprietary mobile threat intelligence.
Yes. Adversary-in-the-middle (AiTM) phishing kits proxy the real login page and capture both the credentials and the session cookie, which lets the attacker skip the MFA prompt. Corrata blocks the IP ranges that host this toolkit infrastructure, which stops the attack before the fake login page loads.
No. Reflex works from the connection a link opens, so it never reads the content of messages, tracks location, scans files, or records browsing history. Traffic that isn’t a threat is never captured or stored, and Corrata’s servers only receive details of threats and the action taken. Corrata is EU-native, incorporated in the EU and headquartered in Dublin, and you can read more about this approach in privacy by architecture.
Most enterprise data now travels over insecure networks. Corrata keeps employee communications private on unsafe cellular and Wi-Fi…
Exploits like Pegasus are no longer limited to nation states. Corrata spots suspicious activity even when nothing shows…
Phones can access the same corporate data as laptops. Corrata ensures only devices known to be secure can…
A short call, a live look at the product, and a straight answer on whether it fits your estate.