Adversary-in-the-Middle (AiTM) protection that keeps phone traffic private on any network
Most enterprise data now travels over insecure networks. Corrata keeps employee communications private on unsafe cellular and Wi-Fi…
Use case
Employees are adopting AI tools faster than policy can keep up, and every upload to an unsanctioned chatbot, file share, or personal email account is a route out for company data. Reflex, Corrata’s on-device engine, blocks those uploads on the phone itself, without reading messages or scanning files.

Every file an employee uploads to an unsanctioned AI chatbot puts internal information, IP, and customer data beyond your control.
Everyday apps add to the risk, from AI agents that can read email and files to ad networks that pass personal data to brokers.

Reflex, Corrata’s on-device engine, inspects network traffic on the phone itself, so it sees where each upload is headed, whether it comes from a mobile app or a web browser. Uploads to unsanctioned AI tools and cloud services are blocked, access to Shadow AI and other unsanctioned services follows your policy, and previously unknown AI apps are discovered and classified as they appear.
Because decisions are made on the device, traffic that isn’t a threat is never captured or stored, and Corrata’s servers only receive details of threats and the action taken. Corrata is also EU-native, incorporated in the EU and headquartered in Dublin.

Shadow AI is a new route out for company data.
Corrata’s own detection data shows how fast it has spread: over six weeks, 84% of customer mobile fleets carried AI traffic, volumes grew by around 40% a month, and 69% of the AI domains detected had never been seen before. Corrata discovers and classifies AI apps as they appear, so you can monitor their use and block unapproved services at the mobile endpoint, well beyond the basic controls available in MDM. For AI agents built into everyday apps, AI Agent Shield detects them live on the device.
Stop sensitive files reaching unsanctioned cloud storage or mail services.
Corrata stops employees uploading sensitive files to unapproved file shares, email, and collaboration services, whether deliberately or by accident, and whether the upload comes through a mobile app or a web browser.
Allow, block, or monitor popular enterprise SaaS.
Typical medium and large organisations use over 100 SaaS services across sales, marketing, finance, and IT, and more of them are now mobile-first. Corrata’s fine-grained controls let you set policies that balance risk with productivity.
Stop personal data leaking through the advertising ecosystem.
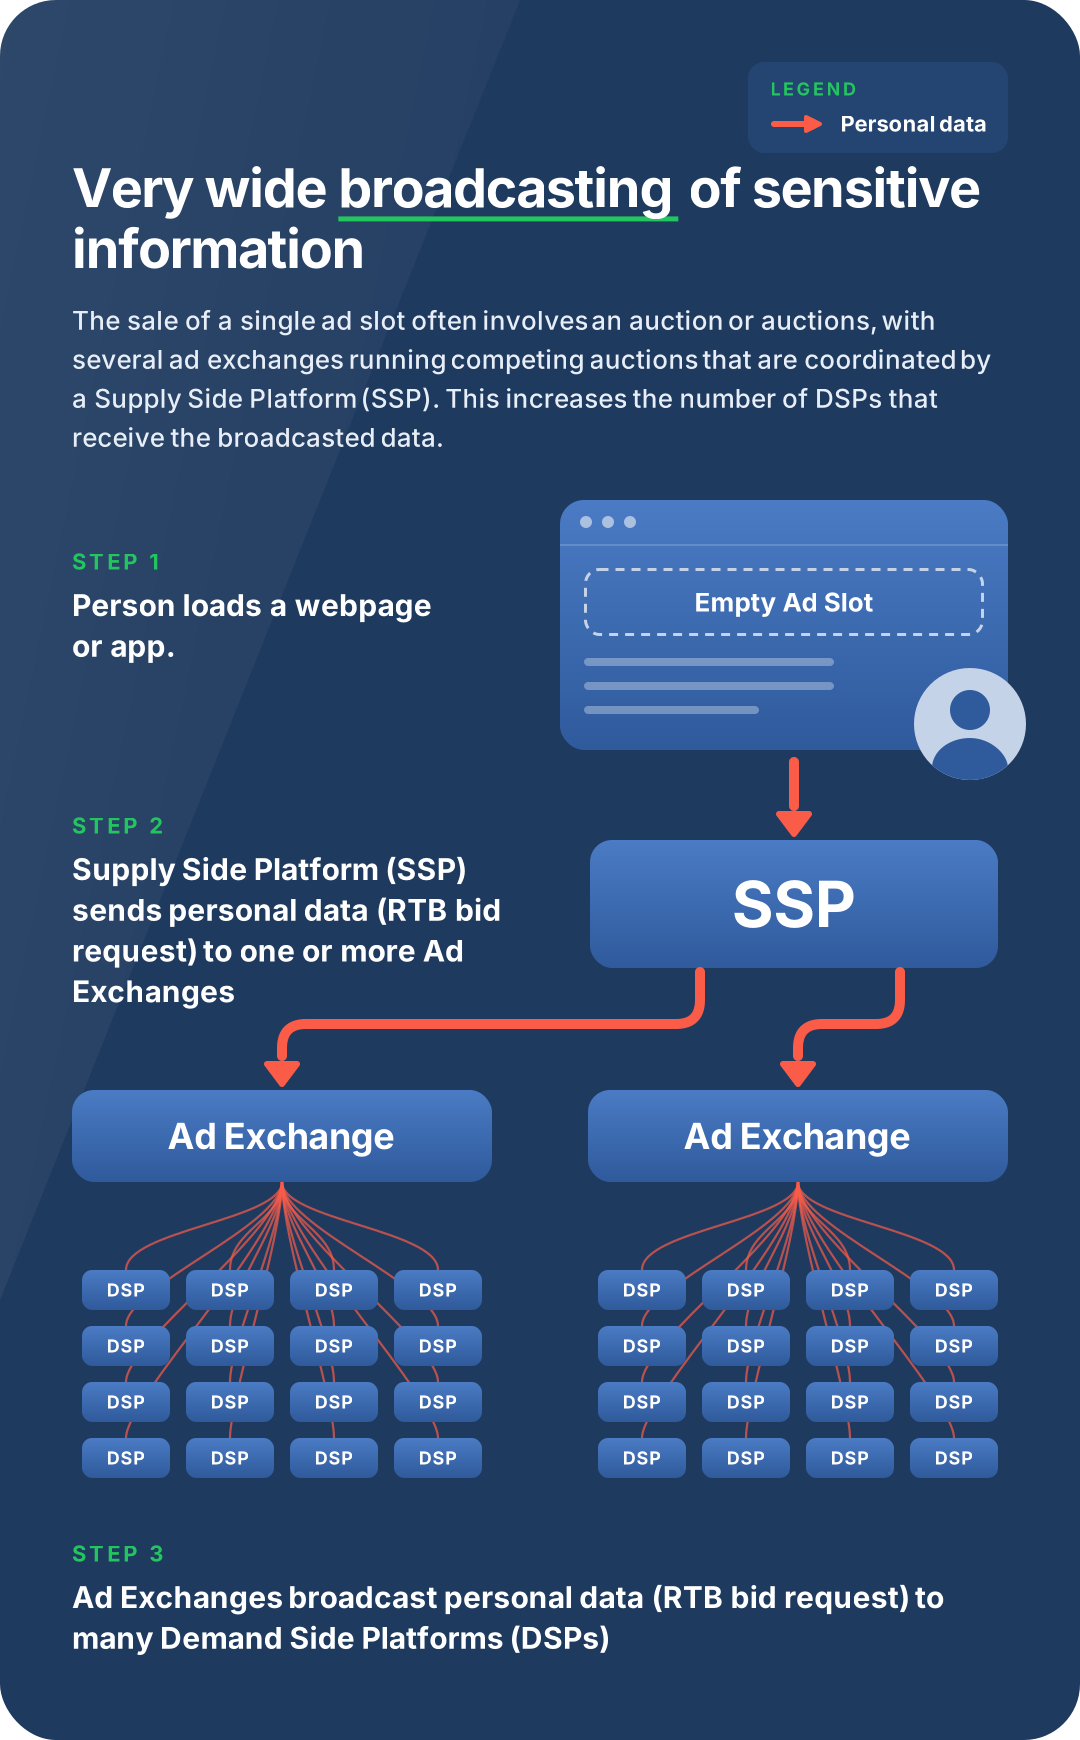
Real-time bidding shares sensitive data, including employee location information, with thousands of unregulated data brokers, and ads can even be used to deliver spyware. Corrata’s ad blocking and location permission controls stop that personal data leaking into an opaque market.
Shadow AI governance is the set of policies and controls that decide which AI tools employees can use and what company data can reach them. On phones, it means seeing the AI services employees actually use, including ones reached through personal accounts, and blocking those you haven’t approved.
Reflex, Corrata’s on-device engine, applies DLP policy on the phone itself, covering uploads through mobile apps and web browsers. Depending on your policy, it can monitor the services in use, block access to unapproved services, and block uploads of sensitive files to unsanctioned AI tools, file shares, email, and collaboration services. Our guide to why legacy DLP fails on phones explains why tools built for laptops miss this.
Yes. Corrata discovers and classifies previously unknown AI apps as they appear, so your policy covers new tools without anyone first having to report them. For AI agents built into everyday apps, Corrata AI Agent Shield detects them live on the device.
Not with Corrata. It decides where an upload is going without reading message content, scanning files, tracking location, or recording browsing history, and its servers only receive details of threats and the action taken. Corrata is EU-native, incorporated in the EU and headquartered in Dublin, and our page on privacy by architecture explains the approach.
Corrata works alongside MDM platforms such as Microsoft Intune and Workspace ONE. MDM manages how devices and apps are configured, while Corrata monitors and controls the AI and cloud services employees actually reach, which goes well beyond the basic controls available in MDM.
Most enterprise data now travels over insecure networks. Corrata keeps employee communications private on unsafe cellular and Wi-Fi…
Exploits like Pegasus are no longer limited to nation states. Corrata spots suspicious activity even when nothing shows…
Phones can access the same corporate data as laptops. Corrata ensures only devices known to be secure can…
A short call, a live look at the product, and a straight answer on whether it fits your estate.