Today, as more and more critical functions migrate to mobile it seems timely to take stock of where we stand as an industry and to provide guidance on the critical threats and vulnerabilities which we face today.
In the ten years since the launch of the iPhone we have learned much about ensuring the integrity and confidentiality of information stored and processed on mobile devices. Apple and Google have made much progress in making iOS and Android appropriate for use in enterprise environments.
It’s clear that the architecture of both the Android and iOS operating systems have helped them avoid many of the security issues which have plagued Windows. Application segregation, in particular, has made it far more difficult for malware to successfully exploit mobile devices. This is because each separate piece of software (‘app’) operates independently and access to data belonging to another app is highly restricted.
In addition apps do not have the kind of administrator privileges which would allow unfettered access to device data and functions. Instead end-users act as administrators of their own devices and are responsible for deciding whether apps have access to specific types of data (e.g. contacts, photos) or functions (camera, location services).
While such end-user control can be a doubleedged sword, Enterprise Mobility Management (EMM) systems can compensate for this. In these circumstances more stringent controls can be imposed and an end-user’s ability to inadvertently compromise a device can be reduced.
Both Apple and Google have shown themselves committed to addressing security issues in a timely fashion. Apple in particular is in the enviable position of having circa 90% of its devices on the last OS version.
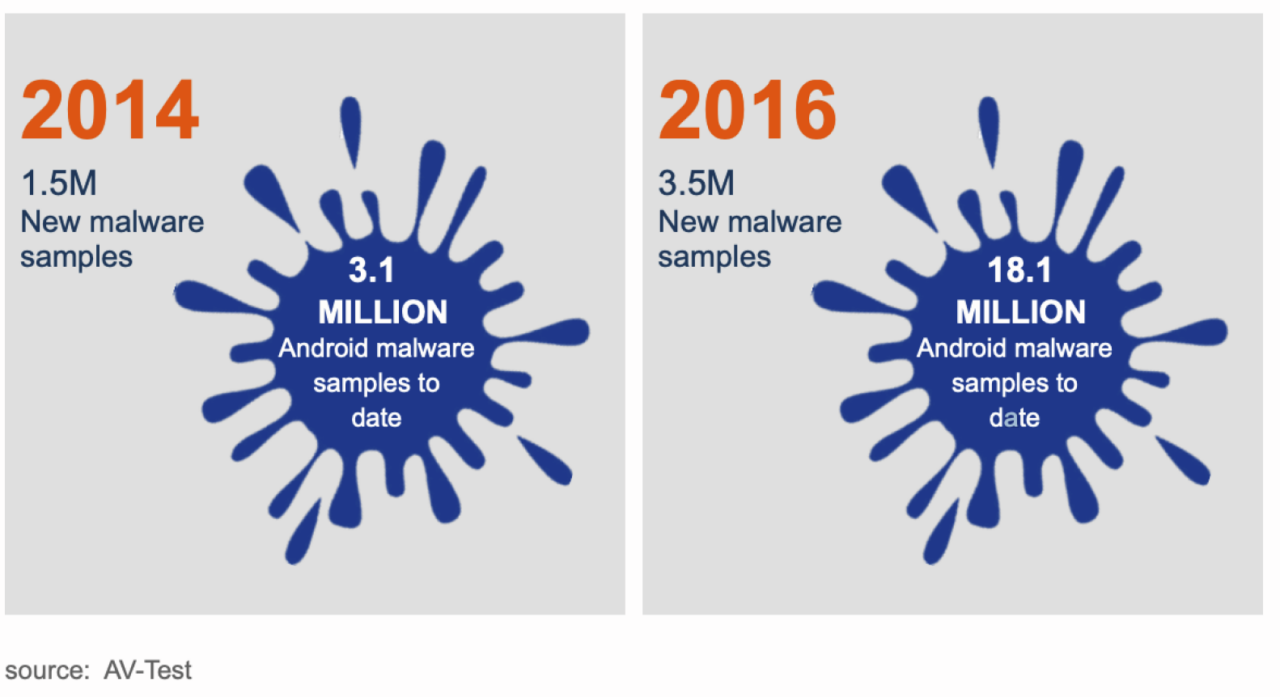
The app store software distribution model is another major security enhancement. In Apple’s case software can only ever (except in limited edge case circumstances such as enterprise distribution) be downloaded to an iOS phone via the App Store. Apps submitted to the App Store are subject to stringent vetting. Malicious apps which do make their way through the process are quickly removed once identified. While Android has also adopted the app store distribution model is continues to allow non Play Store downloads. In addition, Android is inherently more open and as a result the opportunities to introduce malicious code are greater. As a result Android suffers from a non trivial rate of malware infection.